Prove what agents actually did.
When an auditor asks what an agent did, the record is already on file, and the agent can’t rewrite it.
When the auditor asks, what will you show?
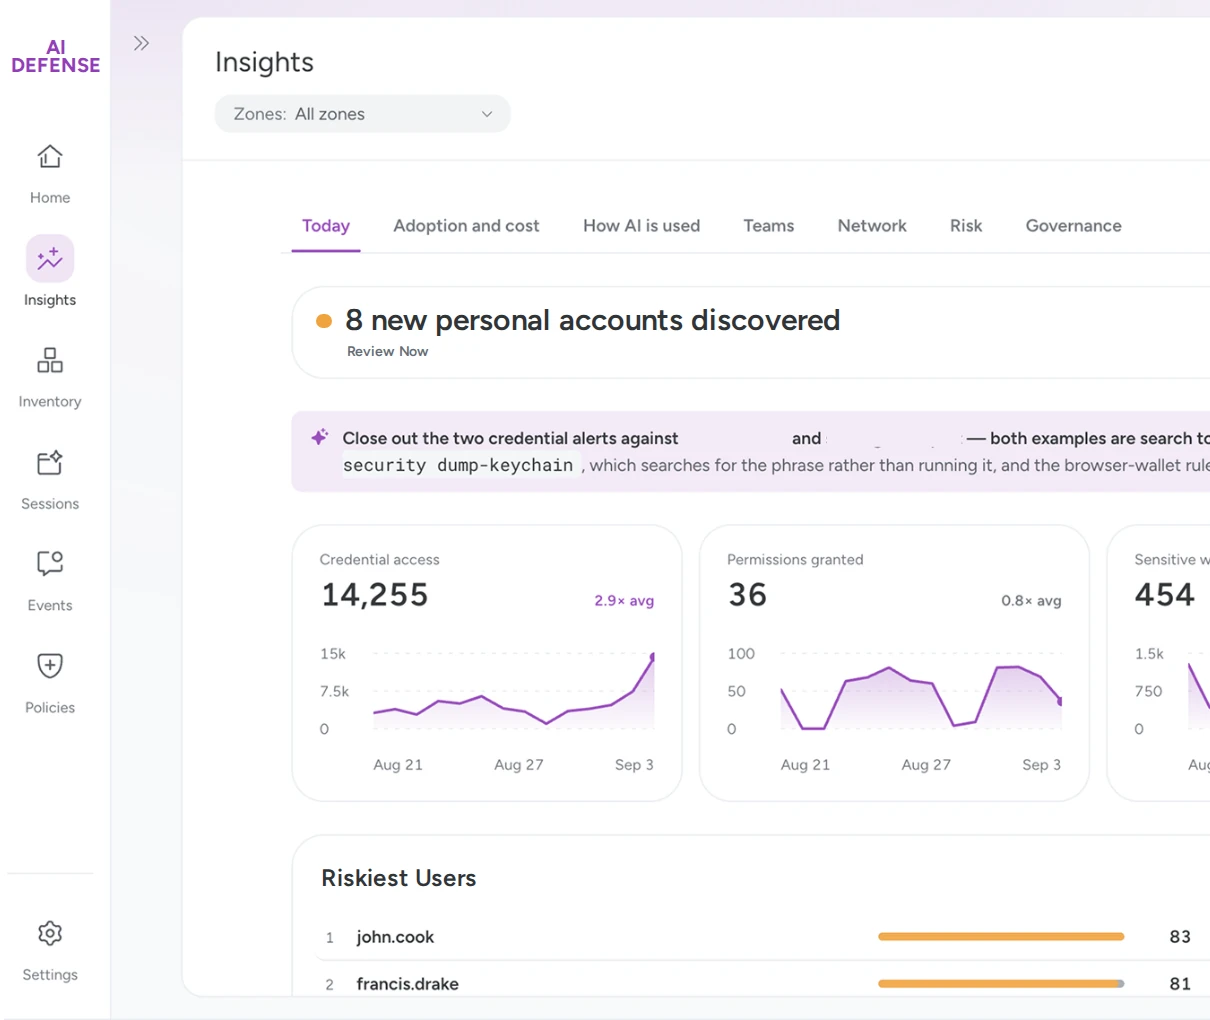
Every organization is now responsible for what its AI agents do. Boards, auditors, and regulators will ask which agents ran, what they touched, and under whose authority. An agent’s own logs can’t answer that. An agent can forge or erase its own account of events. Logs of prompts and tool calls are context, not evidence.
Answering audits shouldn’t pull your developers off their work.
Kernel processes logged vs. agent-logged tool calls
What you get with Sysdig AI Defense
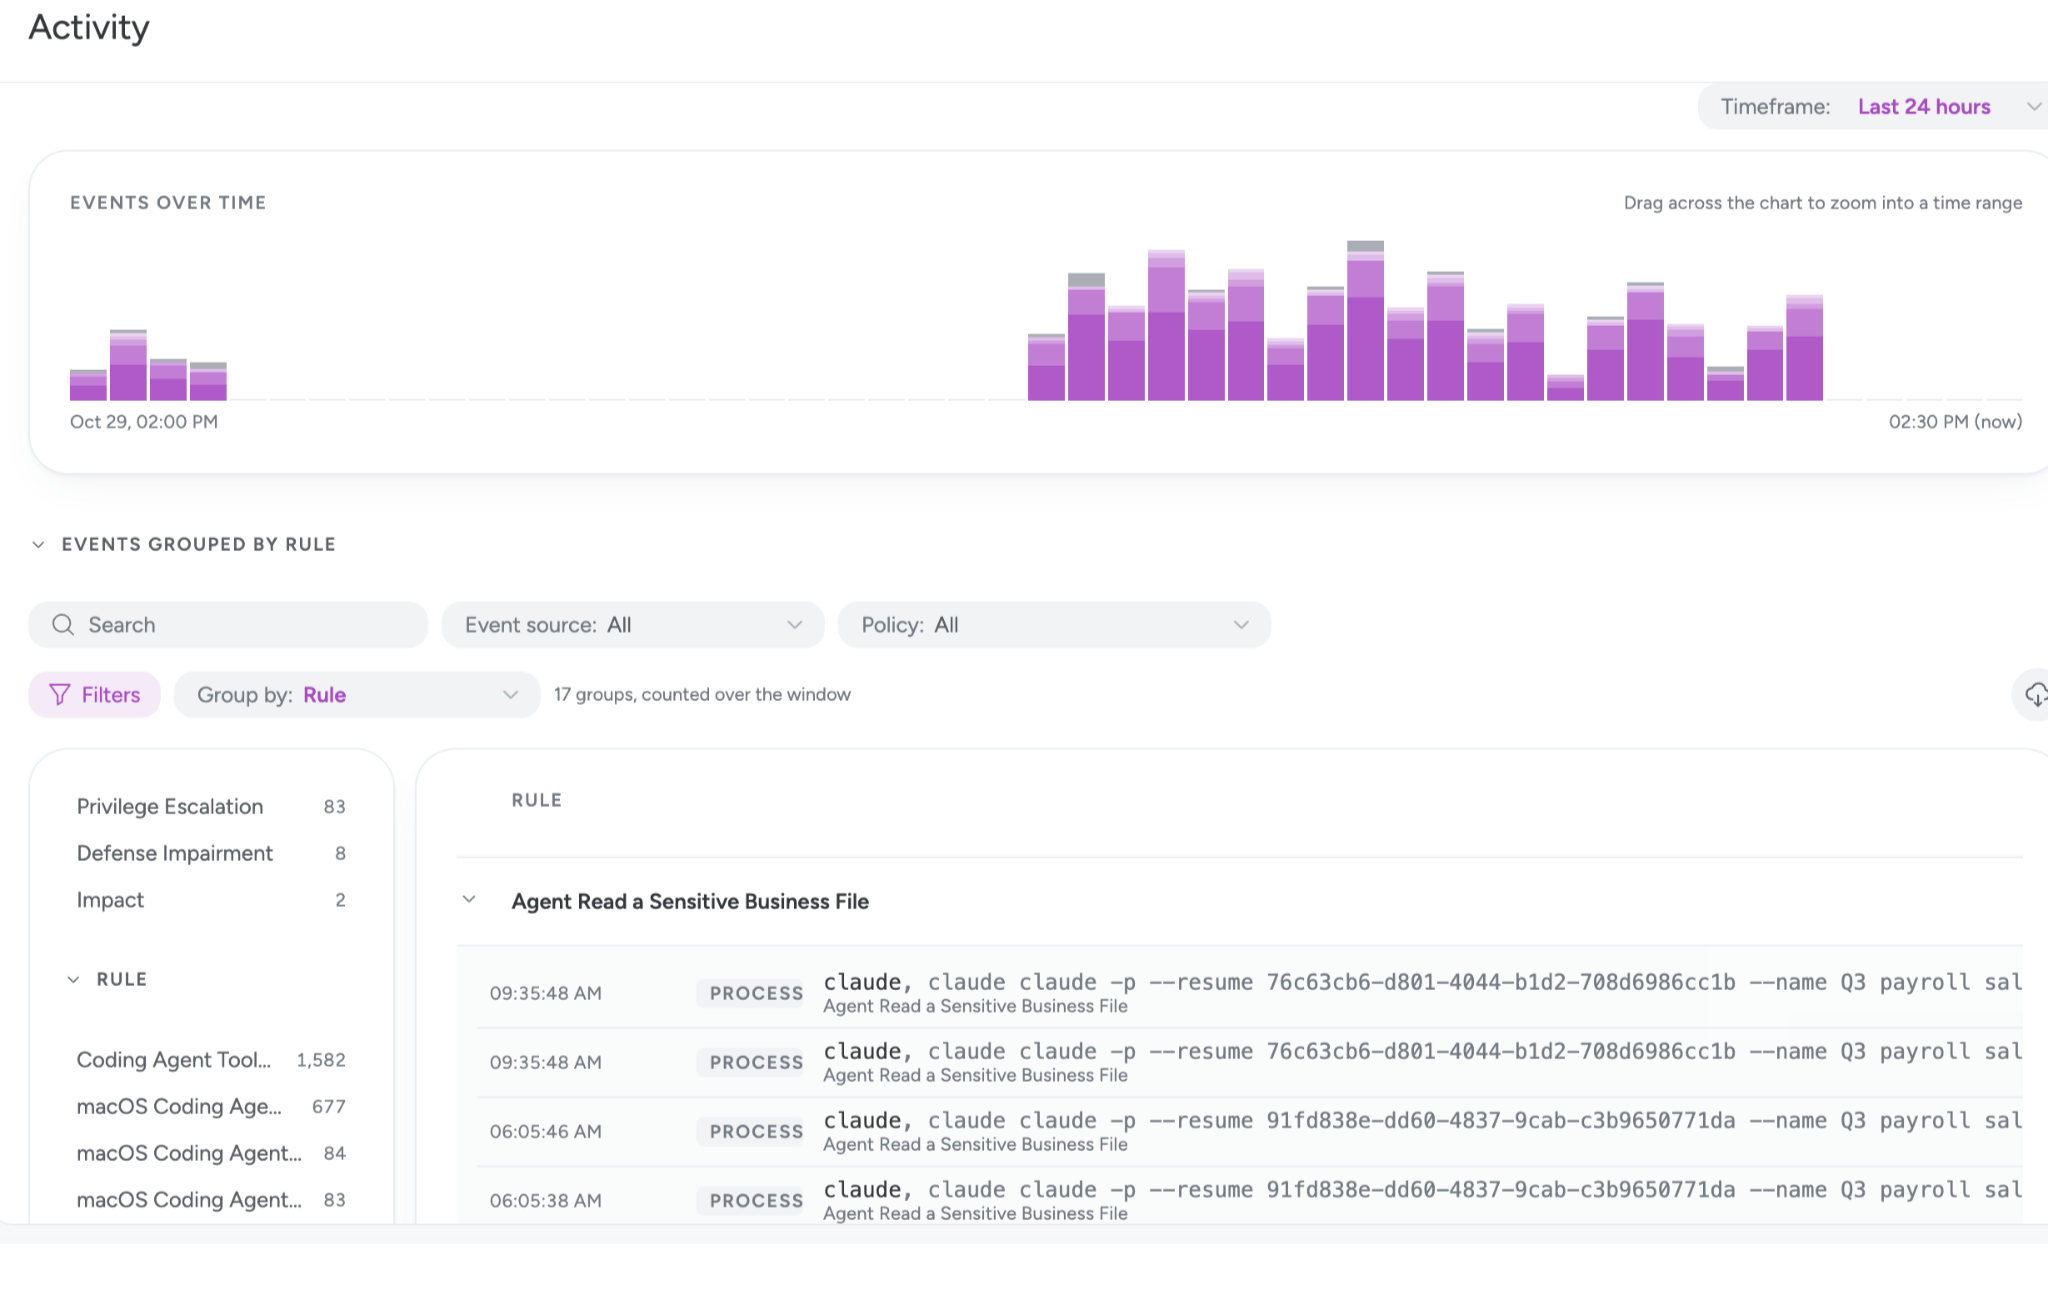
A record the agent can’t edit
Activity is captured at the kernel, below the agent, so a compromised agent can’t tamper with it. Each action is paired with the agent’s own account and traced to the person behind it.
Policy history on file
Start from policy templates mapped to frameworks like the OWASP Top 10 for LLM Applications, then see which policies were applied when and which actions were allowed, approved, or blocked.
Records that fit the audit stack you run
Activity is retained and can be forwarded to your SIEM or other tools, so it sits alongside the rest of your audit records.

Evidence the agent can’t rewrite.
Compliance evidence is only as good as its source. Self-reported agent logs can be incomplete or altered. Network-only records miss local activity. Runtime is where the evidence lives, and AI Defense captures it without slowing the people who use the agents.
See what your agents are actually doing.
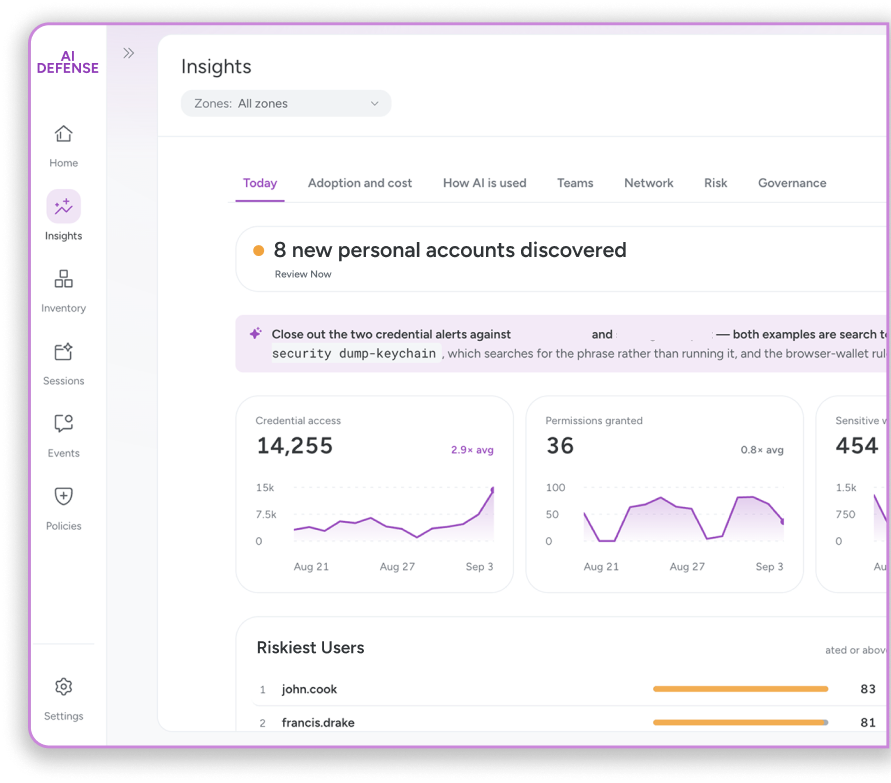
A First Look: Under the Hood of an AI Agent
One month under the hood of an AI agent: what 300+ employee devices revealed about citizen developers, the AI supply chain, governance gaps, runtime control, credentials and model spend.
Read the report
Your Blueprint to Securing AI Workloads, the Right Way
AIBOM: The infrastructure, risks, and how to secure AI models